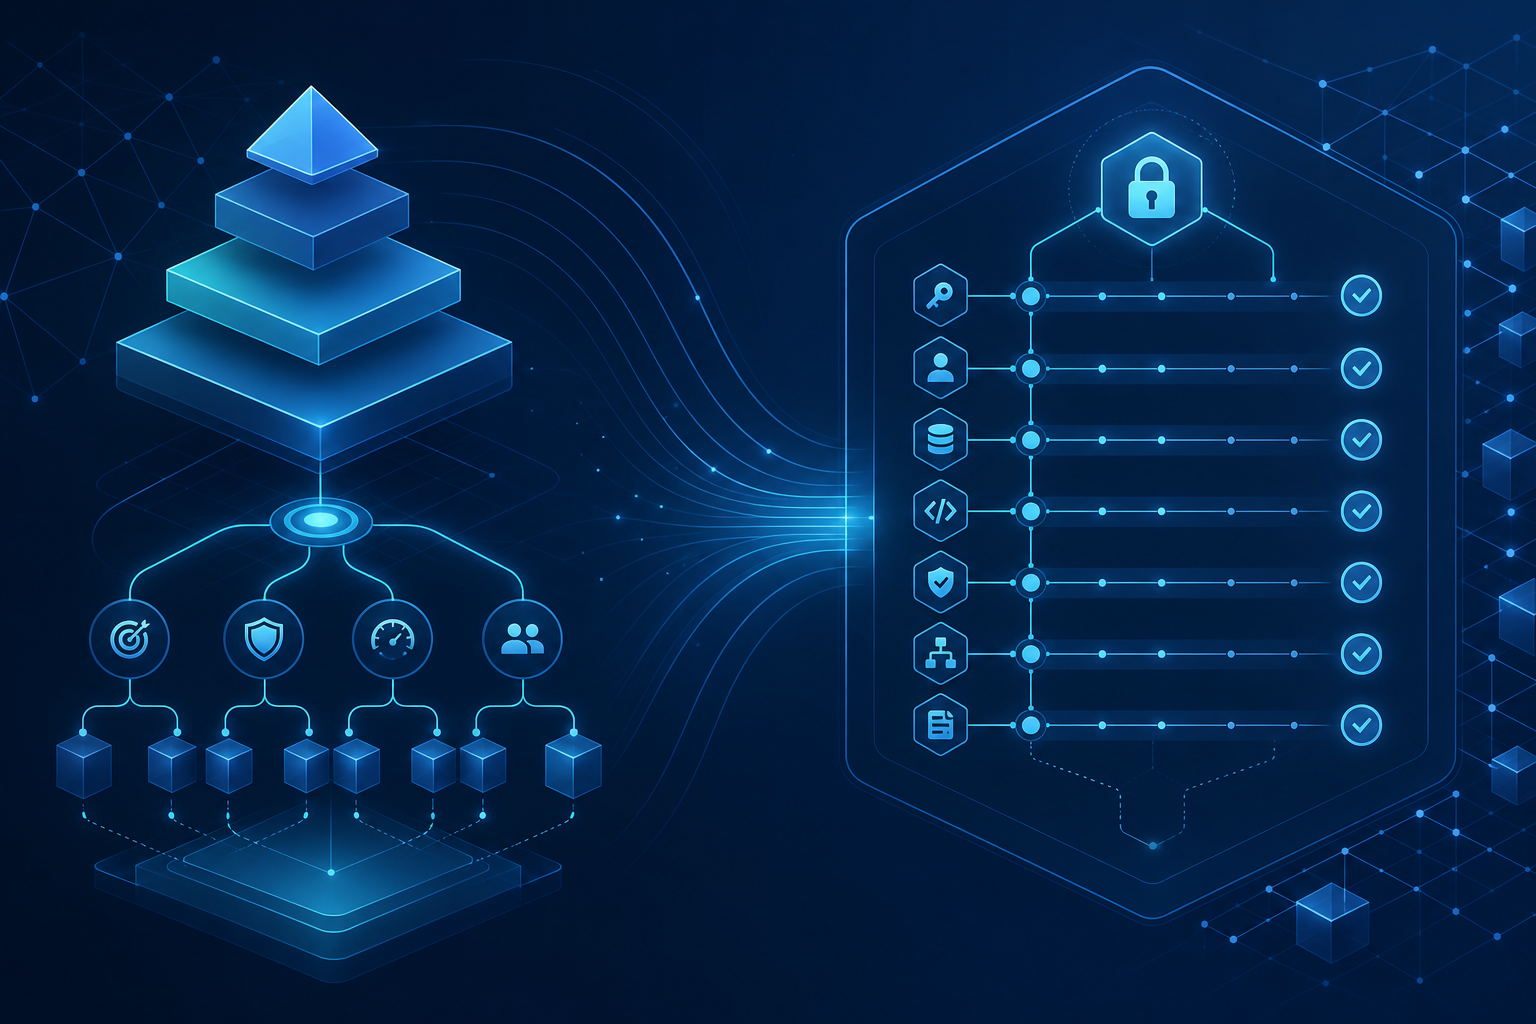
Understand the difference between a test strategy vs test plan while implementing an actionable api security testing checklist to protect endpoints.
When comparing a test strategy vs test plan, the primary difference lies in scope and execution: a test strategy defines the overarching, organizational philosophy and quality standards for an entire system, whereas a test plan details the tactical execution, resource allocation, and schedule for a specific project or release cycle. Understanding this distinction is critical when applying an actionable api security testing checklist to safeguard distributed endpoints against modern vulnerabilities.
- Test strategies establish organizational governance, while test plans manage project-level execution.
- Security testing must be anchored at the strategic level to prevent ad-hoc, fragile validation.
- A structured checklist ensures systematic coverage across authentication, authorization, and data validation.
- Automated vulnerability scanning combined with intelligent test orchestration minimizes manual overhead.
Test Strategy vs Test Plan: Architectural Foundations
Recent industry data suggests that engineering organizations often conflate governance with project scheduling. A test strategy outlines the overarching methodology, risk mitigation approaches, and quality gates that apply across all engineering efforts. In contrast, a test plan addresses specific milestone deliverables, environment setups, and team assignments for a defined sprint or release window.
In practical quality assurance, the strategy acts as the constitutional foundation. It establishes whether your organization mandates shift-left contract testing, automated fuzzing, or continuous compliance scanning. The plan, meanwhile, identifies who runs those suites, on which clusters, and by what deadline. Conflating these two concepts results in fragmented testing efforts where vital concerns like authorization protocols get deferred indefinitely.
| Dimension | Test Strategy | Test Plan |
|---|---|---|
| Primary Scope | Organizational or product portfolio level | Specific project, release, or sprint |
| Author & Ownership | QA Director or Enterprise Architect | QA Lead or Project Test Manager |
| Change Frequency | Infrequent, reviewed quarterly or annually | Dynamic, updated per sprint or release |
| Core Deliverable | Testing standards, tooling, and risk policies | Schedules, test cases, and environment specs |
To establish long-term resilience, engineering teams often integrate modern platforms like AI-powered testing architectures to execute these high-level architectural mandates across diverse deployment pipelines.
How Do Strategic Goals Shape API Security Execution?
Based on current best practices, tactical execution without a cohesive strategy produces inconsistent security testing. When an organization embeds security into its baseline test strategy, individual project plans automatically inherit non-negotiable security tasks. Rather than debating whether penetration tests belong in a two-week sprint, the overarching strategy dictates that every production endpoint must satisfy strict validation thresholds before deployment.
Consider an enterprise handling 150 microservices across multiple cloud regions. If each squad defines testing independently, authorization logic is tested inconsistently. A unified test strategy specifies authentication standards, encryption mandates, and logging rules. The team then crafts a tactical test plan specifying exact staging environments, synthetic datasets, and test schedules to fulfill those enterprise standards.
By establishing this clear separation between your test strategy vs test plan, security transitions from a last-minute audit into an automated, systematic quality gate integrated directly into CI/CD workflows.
The Core API Security Testing Checklist
Modern application programming interfaces handle over 80% of web traffic, making endpoints the primary target for malicious actors. An effective api security testing checklist provides verifiable testing criteria designed to catch OWASP Top 10 vulnerabilities, including broken object-level authorization and mass assignment, before code reaches production environments.
To protect sensitive endpoints, QA teams should audit their microservices against structured security verification items, as outlined below.
1. Authentication and Token Handling
Verify that JSON Web Tokens (JWT) and API keys enforce strict expiration policies and signature validations. Confirm that tokens cannot be manipulated using algorithm switching attacks (such as downgrading RS256 to none) and that revoked credentials reject requests within 500 milliseconds.
2. Broken Object Level Authorization (BOLA)
Test that authenticated users cannot access records belonging to other tenants simply by altering path parameters or UUIDs. Inspect both direct object identifiers and nested endpoints to ensure access control logic evaluates contextual user permissions on every call.
3. Data Exposure and Mass Assignment
Examine payload responses to confirm that back-end services do not leak internal database schemas, password hashes, or unmasked personal information. Ensure that payload injection containing administrative properties (such as role: admin) is rejected by strong request schemas.
4. Rate Limiting and Resource Consumption
Execute stress tests to confirm that endpoints enforce throttling thresholds (e.g., maximum 100 requests per minute per IP address). Validate that rate limits return HTTP status code 429 and prevent denial of service attacks without causing downstream cluster failures.
Teams using dedicated security testing tools for software development often automate this checklist to eliminate reliance on sporadic manual penetration reviews.
Bridging Strategy and Tactics: An Implementation Workflow
Recent architectural studies confirm that security vulnerabilities are up to 15 times cheaper to resolve when detected during integration testing rather than production. Translating enterprise standards into daily sprints requires establishing continuous feedback loops between the governance strategy and tactical execution plans.
- Define Non-Negotiables: Codify baseline compliance rules in the organizational test strategy, including mandatory fuzzing for public endpoints.
- Generate Contextual Test Plans: Instruct development teams to pull standard security test suites directly into their sprint-level test plans.
- Deploy Automated Scanners: Integrate dynamic application security testing (DAST) tools that parse OpenAPI schemas to execute automated abuse cases.
- Track Remediations Continuously: Aggregate failure logs within centralized dashboards to prevent regressions across service updates.
For authoritative guidelines on standardized web service audits, practitioners frequently reference the OWASP API Security Project and security implementation standards from the NIST Special Publication 800-204 series on microservice security.
Executing Your API Security Testing Checklist with Precision
A rigorous api security testing checklist is only as effective as the rigor with which QA teams execute it. Testing teams must combine automated schema validation with deep semantic testing. Running simple positive tests to verify HTTP 200 OK responses is insufficient; robust verification requires injecting malformed headers, unexpected data types, and cross-boundary parameters.
Teams deploying platforms like TestBots benefit from autonomous validation agents that automatically generate negative test scenarios based on live API traffic patterns. Rather than maintaining static assertion scripts that break when endpoints change, intelligent orchestration identifies boundary regressions and authorization anomalies across builds without extensive manual scripting.
When teams deliberately align their high-level test strategy vs test plan, security testing shifts from a reactive roadblock into a predictable, automated baseline that accelerates deployment velocity while safeguarding user data.
Frequently Asked Questions
What is the difference between a test strategy vs test plan?
A test strategy is a high-level, long-term document defining organizational standards, testing methodologies, and quality governance. A test plan is a tactical, project-specific document outlining the scope, schedule, personnel, and environment configurations for an individual software release.
Why is an API security testing checklist essential for agile teams?
An API security testing checklist ensures that development squads systematically test authorization, token lifecycles, and input validation during rapid sprint cycles, preventing critical vulnerabilities from slipping through fast-paced continuous deployment pipelines unnoticed.
How often should an enterprise test strategy be updated?
An enterprise test strategy should be reviewed semi-annually or annually, or whenever the engineering organization adopts fundamental architectural changes such as migrating to microservices, implementing zero-trust networking, or adopting autonomous testing frameworks.
Raj Patel
AI/ML testing researcher exploring the intersection of artificial intelligence and software quality assurance.